
Step-by-Step POS Integration Workflow for Retailers
July 17, 2026
TL;DR:
- Proper POS integration connects sales systems with inventory, accounting, and payment platforms, reducing manual errors. Effective preparation, thorough testing, and clear data ownership are essential to avoid costly failures and ensure smooth operation. Using tokenization and outline source-of-truth agreements enhance security and compliance during the process.
A step-by-step POS integration workflow is the systematic process of connecting your point-of-sale system to inventory management, accounting, ecommerce, and payment platforms so data flows automatically between them. Done correctly, this process eliminates manual data entry, reduces reconciliation errors, and gives operations managers a single, accurate view of sales and stock. The industry standard term for this discipline is “POS system integration,” and it covers everything from hardware compatibility checks to post-launch monitoring. This guide walks IT professionals and operations managers through each phase, with the technical depth needed to execute a production-grade rollout.
What prerequisites and system requirements are essential before POS integration?
Preparation determines whether your integration succeeds or fails before a single API call is made. Skipping this phase is the single fastest way to create expensive problems mid-project.
Audit your existing systems
Start by cataloging every system that will touch the integration: your POS terminals, payment hardware, ERP, inventory platform, ecommerce storefront, and accounting software. Document the software versions, API capabilities, and data formats each system uses. This inventory becomes your integration map.
Hardware compatibility is non-negotiable. Confirm that your payment terminals support EMV chip, NFC contactless, and your target card schemes. Check that your network infrastructure can handle the latency requirements of real-time payment authorization. A terminal running outdated firmware will fail certification tests and delay your go-live date.
Assess data quality before you start
Data cleanup costs between $2,000 and $10,000 are typical before integration begins, covering duplicate record removal and format normalization. That figure reflects a real operational cost that most project budgets underestimate. Poor data quality upstream creates cascading errors downstream, so budget for it explicitly.
Run deduplication checks on your product catalog, customer records, and supplier data. Standardize date formats, currency fields, and SKU naming conventions across every system. Define which system holds the authoritative record for each data entity before development starts.
Choose your integration approach
Three primary approaches exist for connecting POS systems to business platforms:
| Approach | Best for | Trade-offs |
|---|---|---|
| Native connector | Standard POS platforms with pre-built modules | Fastest setup; limited customization |
| Middleware platform | Multi-system retail environments | Flexible; adds a dependency layer |
| Custom API build | Unique workflows or legacy systems | Full control; highest cost and time |
Define your success metrics before selecting an approach. Metrics worth tracking include transaction sync latency, error rate per 1,000 transactions, inventory accuracy percentage, and time-to-reconcile for end-of-day reports.
What does the step-by-step POS integration workflow look like in practice?
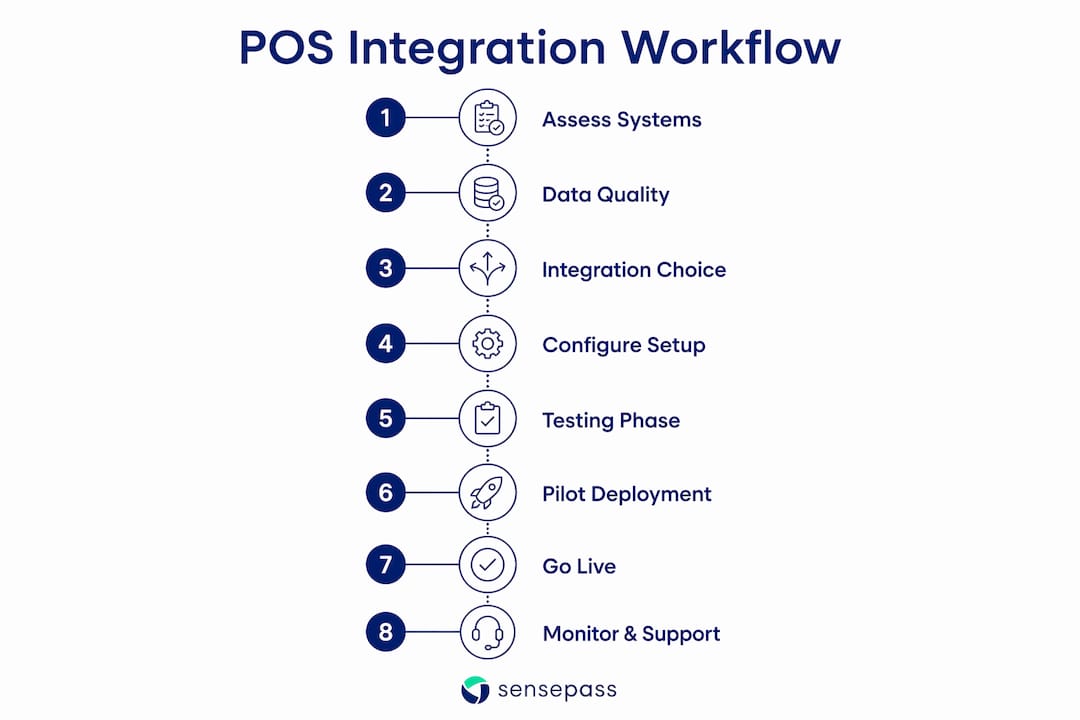
A complete POS workflow consists of eight critical phases. Each phase has a defined output that gates the next phase. Skipping ahead creates technical debt that surfaces at the worst possible moment, typically during peak trading.
The eight phases in sequence
-
System audit and requirement definition. Document every data flow in your current environment. Map where sales data originates, where it needs to land, and at what frequency. Produce a requirements document that all stakeholders sign off on before any development begins.
-
Hardware and platform compatibility verification. Confirm EMV terminal firmware versions, network switch capacity, and API version support for every connected platform. Request sandbox credentials from your payment processor at this stage.
-
Data mapping and schema definition. Define the field-level mapping between systems. A product record in your ERP may use a 12-digit internal SKU, while your ecommerce platform uses a slug. Map every field, including nulls and optional fields, to prevent silent data loss.
-
Integration strategy selection. Choose between native connectors, middleware, or custom API based on your audit findings. Omnichannel retailers benefit from a hybrid sync pattern: near real-time for inventory events and batched processing for financial data. This balances stock accuracy with ERP performance.
-
Environment configuration and staging setup. Build a staging environment that mirrors production as closely as possible. Configure your integration layer, set up authentication tokens, and load a representative sample of production data for testing.
-
Sandbox and integration testing. Run unit tests on individual API endpoints, then integration tests across connected systems. Test edge cases: zero-quantity items, refunds, split tenders, and network timeouts. Standard POS setups require 1–2 weeks of testing; complex enterprise implementations need 4–8 weeks. Cutting this phase short is the primary cause of post-launch incidents.
-
Phased cutover and go-live. Execute your go-live in phases, starting with a single store or register. Have a documented rollback plan ready before you flip the switch. A rollback plan is not optional; it is the difference between a recoverable incident and a business-stopping outage.
-
Post-launch hypercare and monitoring. Monitor error rates, sync latency, and data discrepancies for at least two weeks after go-live. Set alerting thresholds so your team catches problems before customers do.
Pro Tip: Create an integration runbook that documents every configuration setting, credential location, and rollback procedure. This document saves hours during an incident and is essential for onboarding new team members.
The table below shows recommended testing durations by implementation complexity:
| Implementation type | Recommended testing duration |
|---|---|
| Single-store, standard POS | 1–2 weeks |
| Multi-location retail chain | 3–4 weeks |
| Enterprise with ERP and ecommerce | 4–8 weeks |
How do you handle errors, compliance, and security during POS integration?
Failed API calls are inevitable in any distributed system. Your architecture must account for them from day one, not as an afterthought. The two mechanisms that prevent silent data loss are dead-letter queues and exponential backoff retry logic.
A dead-letter queue captures failed messages so they can be reviewed and reprocessed manually. Exponential backoff prevents your system from hammering a temporarily unavailable endpoint, which would compound the original failure. Without both mechanisms, a 30-second network blip can create inventory discrepancies that take days to find and fix.
Defining your source of truth
Explicit agreement on which system is the master record for each data entity prevents the most common and costly integration failure: sync conflicts. Decide before development begins whether your ERP or your POS holds the authoritative product catalog. Decide whether your ecommerce platform or your POS owns customer records. Document these decisions formally. Changing them mid-project is expensive.
PCI DSS compliance and tokenization
Tokenization architectures reduce PCI DSS obligations by limiting cardholder data exposure. When your POS never stores or transmits raw card numbers, your compliance scope shrinks significantly. This is the most cost-effective security strategy available to retail IT teams.
Tokenization limits the cardholder data that flows through your integration, which directly reduces your PCI DSS audit scope. Fewer systems in scope means lower compliance costs and a smaller attack surface. Pair tokenization with role-based access control and audit logging on every system that touches payment data.
Key security practices for your integration:
- Implement role-based access control so only authorized personnel can modify integration configurations.
- Enable audit logging on all payment-adjacent systems and retain logs for the period your compliance framework requires.
- Use retail payment security practices to minimize the number of systems that touch raw card data.
- Conduct a PCI DSS scoping exercise before go-live to confirm which systems fall inside your cardholder data environment.
Pro Tip: Ask your payment processor or gateway whether they support point-to-point encryption at the terminal. P2PE combined with tokenization can reduce your PCI DSS scope to the smallest possible footprint.
73% of POS integration failures stem from inadequate testing environments, unresolved sync conflicts, missing rollback plans, and poor documentation. That statistic means software selection is rarely the deciding factor in project success. Process discipline is.
What testing and deployment strategies reduce go-live risk?
Effective testing follows a staged sequence. Each stage validates a different layer of the system before you expose real transactions to the new integration.
Recommended testing sequence
- Unit testing. Test individual API endpoints in isolation. Confirm that each call returns the expected response for both valid and invalid inputs.
- Integration testing. Test data flows between connected systems. Confirm that a sale recorded in the POS appears correctly in your ERP and inventory platform within the expected sync window.
- Volume testing. Simulate peak transaction loads to confirm the integration holds under pressure. A system that works for 10 transactions per minute may fail at 200.
- User acceptance testing (UAT). Have store managers and cashiers run real-world scenarios in the staging environment. They will find edge cases your technical team missed.
Parallel running and pilot deployment
Run your old and new systems in parallel during the pilot phase. This means processing real transactions through both systems and comparing outputs daily. Discrepancies surface quickly, and you still have the legacy system as a fallback.
Choose a pilot location that represents your typical store profile. Avoid piloting in your highest-volume location first. A mid-volume store gives you real data without maximum risk.
Post-pilot monitoring should track:
- Sync error rate per 1,000 transactions
- Inventory accuracy compared to physical counts
- End-of-day reconciliation time versus baseline
- Staff-reported issues logged through a structured feedback channel
A phased cutover rolls out the new integration store by store over several weeks. A big-bang cutover switches all locations simultaneously. Phased cutover is lower risk for multi-location retailers. Big-bang cutover is acceptable only when all locations share identical configurations and your team has completed a full pilot with zero critical defects.
Staff training deserves its own timeline. Schedule training sessions no more than five days before go-live so knowledge stays fresh. Provide a one-page quick-reference card for cashiers covering the most common scenarios: refunds, split tenders, and offline mode.
Key Takeaways
A successful POS integration depends on preparation, disciplined testing, and documented error handling far more than on software selection alone.
| Point | Details |
|---|---|
| Prepare data before integration | Budget $2,000–$10,000 for data cleanup; poor records create downstream errors that are costly to fix. |
| Follow all eight phases | Skipping any phase, especially testing, is the primary cause of post-launch failures and sync conflicts. |
| Define your source of truth | Agree on master records for products, customers, and inventory before development begins. |
| Use tokenization for compliance | Tokenization reduces PCI DSS scope and lowers compliance costs across your entire payment environment. |
| Test at scale before go-live | Enterprise integrations require 4–8 weeks of testing; insufficient testing causes the majority of post-launch incidents. |
What I’ve learned from watching POS integrations go wrong
After working through multiple retail POS integration projects, the pattern that stands out most is this: teams that invest heavily in software selection and rush the documentation phase almost always struggle at go-live. The teams that spend two extra weeks writing runbooks and defining data ownership agreements ship cleaner, faster, and with fewer incidents.
The uncomfortable truth about POS integration is that the technical work is rarely the hard part. The hard part is getting your ERP team, your store operations team, and your payment processor to agree on a single source of truth for inventory before anyone writes a line of code. I’ve seen integrations delayed by months because that conversation happened too late.
Automation is valuable, but human oversight during the first two weeks post-launch is irreplaceable. Set up a daily sync-check ritual where someone manually compares a sample of transactions across systems. This catches edge cases that automated alerts miss. The retail payment workflow you build is only as reliable as the monitoring you put around it.
One trend worth watching: the shift toward processor-agnostic payment layers is changing how retailers approach integration. Instead of building a direct connection to a single processor, forward-looking IT teams are building to an orchestration layer that can route transactions across multiple processors. This gives you negotiating leverage and eliminates single-processor dependency. That architectural decision is worth making at the design phase, not after go-live.
— Vlad
How Sensepass fits into your POS integration strategy
Sensepass is an orchestration layer and payment gateway built specifically for omnichannel retailers. It connects directly to major POS platforms including NetSuite, SuiteCommerce, Oracle Xstore, Aptos, Shopify POS, BigCommerce, Storis, NCR, and Dynamics365, among others.
Sensepass is processor-agnostic, giving you access to 50+ card processors so you can choose the best rates and terms without rebuilding your integration. It supports digital wallets (PayPal, Venmo, WeChat, Apple Pay, Google Pay, Alipay, Amazon Pay), BNPL options (Klarna, Sezzle, ZIP, Splitit, Afterpay), financing through WeGetFinancing and Affirm, crypto payments via BitPay and Coinbase, and pay-by-bank through Trustly and LinkMoney. For retailers building or upgrading their payment infrastructure, the complete omnichannel payments guide covers how these capabilities connect across in-store, self-checkout, and online channels. You can also review payment gateway selection tips to identify the right configuration for your store environment.
FAQ
What is a POS integration workflow?
A POS integration workflow is the structured process of connecting a point-of-sale system to other business platforms such as inventory, accounting, and ecommerce. It follows defined phases from system audit through post-launch monitoring to ensure data flows accurately between systems.
How long does a POS integration take to complete?
Standard single-store integrations typically require 1–2 weeks of testing alone, while enterprise implementations need 4–8 weeks. Total project timelines vary based on system complexity, data quality, and the number of connected platforms.
What causes most POS integration failures?
73% of failures trace back to inadequate testing environments, unresolved sync conflicts, missing rollback plans, and poor documentation. Software selection is rarely the root cause.
What is a source of truth in POS integration?
A source of truth is the single system designated as the master record for a specific data entity, such as product catalog, customer records, or inventory levels. Defining this early prevents sync conflicts and data quality issues throughout the integration lifecycle.
How does tokenization help with PCI DSS compliance?
Tokenization replaces raw card numbers with non-sensitive tokens so your integration never stores or transmits cardholder data. This reduces the number of systems in your PCI DSS compliance scope, lowering both audit complexity and security risk.
Recommended
- POS Payment Workflow Modernization for Retailers – Omnichannel payments at the Point Of Sale | Sensepass
- Retail POS Payment Optimization for Higher Conversions – Omnichannel payments at the Point Of Sale | Sensepass
- Payment Gateway Integration Guide for Omnichannel Retailers – Omnichannel payments at the Point Of Sale | Sensepass
- How Do I Integrate Afterpay into Shopify Without Cards? (Setup Guide)

 New York Office
260 Madison Ave Suite 8018 New York NY 10016

